


Cyberattacks via Microsoft Teams: IT Support as a Pretext
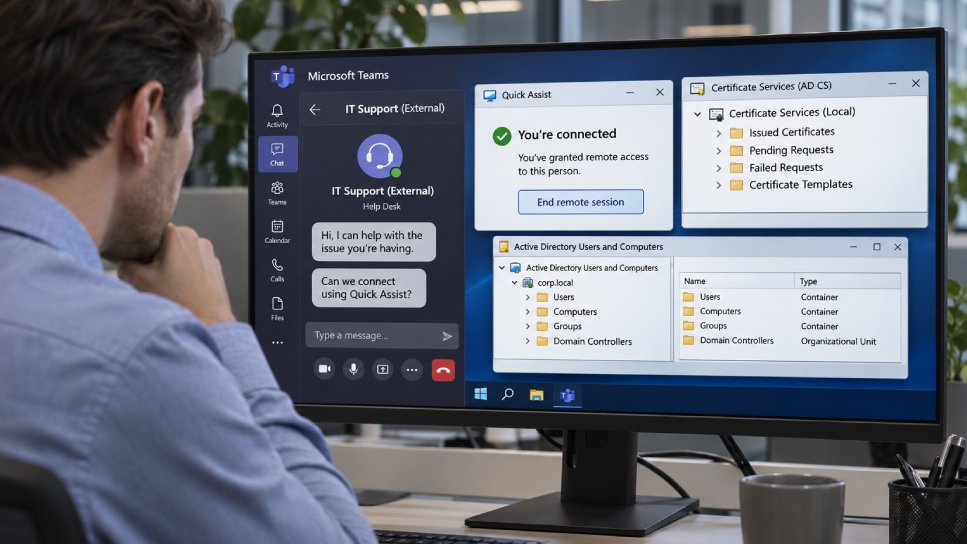
Attackers have impersonated IT support through Microsoft Teams, convincing employees to grant them remote control of their computers. This tactic allowed the perpetrators to exploit insecure settings of the Active Directory Certificate Services (AD CS) to obtain login certificates for privileged accounts. Microsoft has investigated two such incidents in a recent report, one of which led to significant data loss for a company. The attackers utilized the remote desktop feature to gain access to employees' systems. Through this method, they were able to access not only personal data but also critical corporate resources.
The use of Microsoft Teams as a communication platform for these attacks highlights how cybercriminals misuse legitimate tools to achieve their goals. A central aspect of the attacks was the exploitation of insecure AD CS settings. This vulnerability enabled the attackers to generate login certificates that allowed access to highly privileged accounts, including a domain controller. Such accounts have extensive permissions within the corporate infrastructure, underscoring the severity of the attacks. Microsoft has informed the affected companies about the incidents and recommends reviewing the security configurations of their AD CS.
Investigations into the incidents have shown that many companies lack the necessary security measures to protect against such attacks. The need to update security policies and conduct employee training is considered urgent. The attacks are part of a larger trend where cybercriminals use social engineering techniques to gain access to corporate networks. The combination of phishing and the exploitation of remote access technologies has increased in recent years. Experts warn that such attacks could become more frequent in the future as more companies rely on remote work and digital communication.
To minimize risks, companies should ensure that their employees are aware of the dangers of social engineering. Regular training and security audits are crucial to improving the security posture. Microsoft has also emphasized that implementing multi-factor authentication (MFA) is an effective measure to enhance security. The incidents have reignited discussions about the security of cloud services and their integration into corporate structures. Many companies are increasingly relying on cloud-based solutions, which expands the attack surface for cybercriminals.
The need to strengthen security protocols and regularly review infrastructure is deemed essential by security experts. Microsoft has announced that it will provide an update to its security protocols by the end of 2026 to better protect users from such attacks. The new features are intended to help companies secure their systems against unauthorized access and ensure the integrity of their data. The vulnerability exploited in the current incidents could potentially affect thousands of companies that rely on Microsoft technologies. The exact number of affected systems is currently being assessed as Microsoft continues to work on improving its security solutions.
These incidents highlight the ongoing threat of cyberattacks and the necessity for companies to take proactive measures. The security landscape is expected to become increasingly challenging as attackers develop more sophisticated methods to infiltrate corporate networks. Microsoft has emphasized in its report that raising employee awareness of security risks and implementing robust security measures are crucial to preventing future attacks. Companies are urged to rethink and adapt their security strategies to meet the new challenges in cybersecurity.
💬 Comments (0)
No comments yet. Be the first to comment!