


Google Session Hijacking: Phishing Campaign Discovered
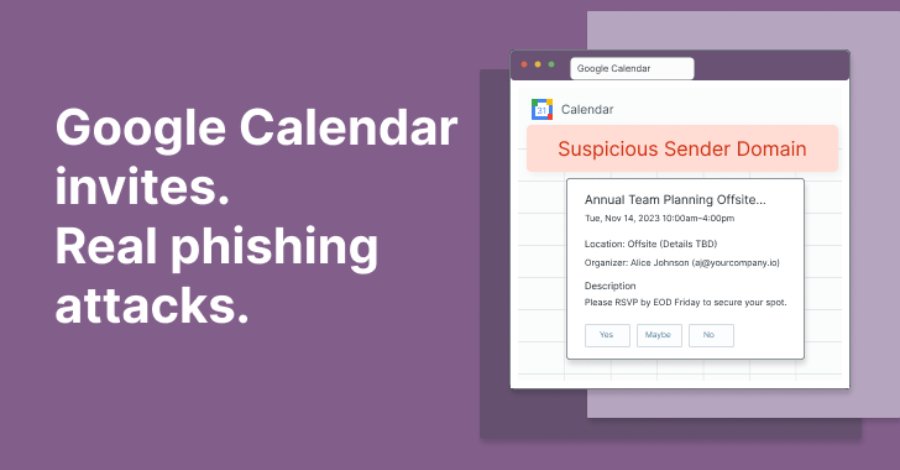
Since mid-August 2026, a phishing operation has been underway aimed at stealing active Google sessions from corporate users. This campaign employs a sophisticated technique to bypass security measures typically used to verify links. The threat research teams at Material Security have uncovered these activities and, as part of their initiative "Operation CloudFire", have already taken down hundreds of the attackers' domains. The attackers have managed to craft their links in such a way that they appear safe during conventional security checks. This poses a significant challenge for IT security departments, as the usual indicators of phishing do not apply.
The campaign has focused on companies utilizing Google services, aiming to obtain sensitive information. Material Security has documented a variety of attacks enabled by these phishing techniques in recent months. The attackers use fake calendar invitations and live proxies to entice users into entering their credentials. This method has proven particularly effective, as it is often embedded within legitimate communication streams. Material Security's security researchers have noted that the campaign targets not only large corporations but also smaller firms.
Attackers employ a range of tactics to reach their audiences, including social engineering and tailored phishing messages. This approach increases the likelihood that users will click on the fraudulent links. As part of Operation CloudFire, Material Security has not only taken down domains but also developed comprehensive training programs for companies. These programs aim to educate employees about the dangers of phishing and help them recognize suspicious activities. The initiative seeks to improve the overall security posture of companies and minimize the risks posed by such attacks.
The threat posed by this phishing campaign should not be underestimated. According to Material Security, the attackers have reached thousands of users in recent months. The exact number of affected accounts is currently unknown; however, it is estimated that the attackers have been able to access a significant amount of sensitive data. The security situation remains tense as the attackers continue to develop new methods to refine their attacks. Companies are urged to review their security protocols and ensure that their employees are informed about the latest threats.
Implementing multi-factor authentication is considered one of the most effective measures to protect against such attacks. Material Security plans to publish the results of their investigations in the coming weeks. These reports are expected to contain detailed information about the attackers' methods and the impact on affected companies. Security researchers emphasize the need to take proactive measures to minimize the risks of phishing attacks.
The campaign has already led to an increase in security incidents among companies using Google services. The exact number of incidents is currently being recorded; however, it is clear that the threat must be taken seriously. Companies should adjust their security strategies to better prepare against such attacks. Material Security has taken down over 300 of the attackers' domains in recent months to mitigate the impact of the campaign.
💬 Comments (0)
No comments yet. Be the first to comment!