


AI-Powered Attacks on BFSI Sector in India
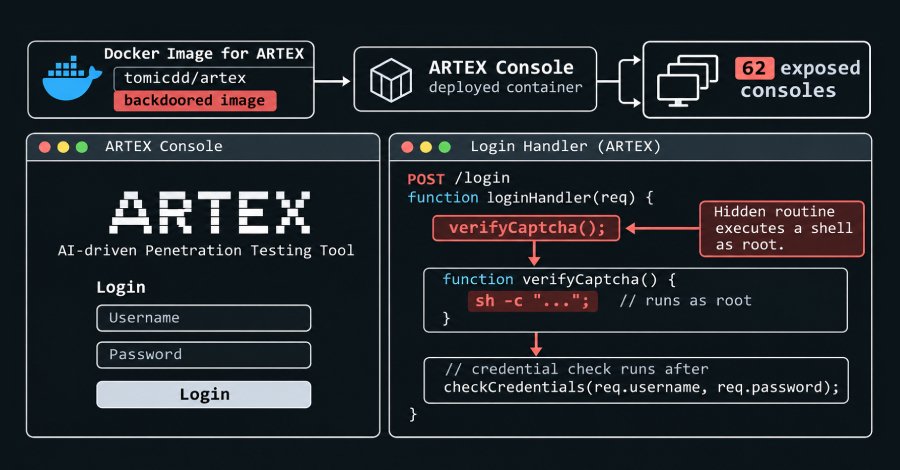
The Indian Computer Emergency Response Team (CERT-In) has issued a warning regarding active attacks from a threat actor known as Crafty Falcon. These attacks specifically target organizations in the Banking, Financial Services, and Insurance (BFSI) sector. The threat is described as active and ongoing, utilizing publicly available, AI-powered offensive security tools. Crafty Falcon employs a variety of techniques to infiltrate the systems of BFSI organizations. The attacks include the use of backdoor methods that allow attackers to gain root access to the affected systems.
CERT-In has urged the affected organizations to review and strengthen their security measures. The threat posed by Crafty Falcon is not new; however, the increasing availability of AI tools has made the attacks more efficient. CERT-In emphasizes that the attackers are capable of quickly adapting their tactics to circumvent security precautions. This dynamic presents a significant challenge for the cybersecurity strategies of the affected companies. The BFSI sector in India is particularly vulnerable to such attacks, as it processes large amounts of sensitive data.
The attackers aim to steal financial information or sabotage systems, which can lead to substantial financial losses. CERT-In has called on companies to update their security protocols and conduct employee training to raise awareness of such threats. In addition to technical measures, CERT-In recommends that companies perform regular security audits and vulnerability assessments of their systems. The implementation of multi-factor authentication processes is also deemed necessary to prevent unauthorized access. These steps are crucial to ensure the integrity of the systems and to detect potential attacks early.
The use of AI in cyberattacks is a growing problem observed not only in India but globally. CERT-In has stressed that the threat from AI-powered attacks is expected to increase in the coming years. Companies must proactively prepare for these developments to strengthen their security architectures. The Indian government has already taken steps to enhance cybersecurity in the BFSI sector, including initiatives to promote collaboration between various security agencies and the private sector.
This collaboration aims to facilitate the exchange of information regarding threats and vulnerabilities. The current warning from CERT-In comes at a time when cybercrime in India has reached a new peak. Reports indicate a 30% increase in cyberattacks in 2025 compared to the previous year, with the BFSI sector being particularly affected, underscoring the urgency of the current warning. The security gap exploited by Crafty Falcon's attacks has not yet been fully identified.
However, CERT-In is working closely with affected companies to analyze vulnerabilities and develop appropriate countermeasures. The agency has already issued initial recommendations to mitigate risks. Indian authorities plan to further raise awareness of cybersecurity in the BFSI sector. Planned training programs aim to help employees recognize potential threats early and respond appropriately. These programs are set to be implemented in several phases by the end of 2026. The situation highlights the necessity for companies in the BFSI sector to continuously adapt and improve their security strategies. CERT-In will continue to monitor developments in cyber threats and inform the public about new risks.
💬 Comments (0)
No comments yet. Be the first to comment!