


Security Vulnerability in Next.js Enables Server Code Execution
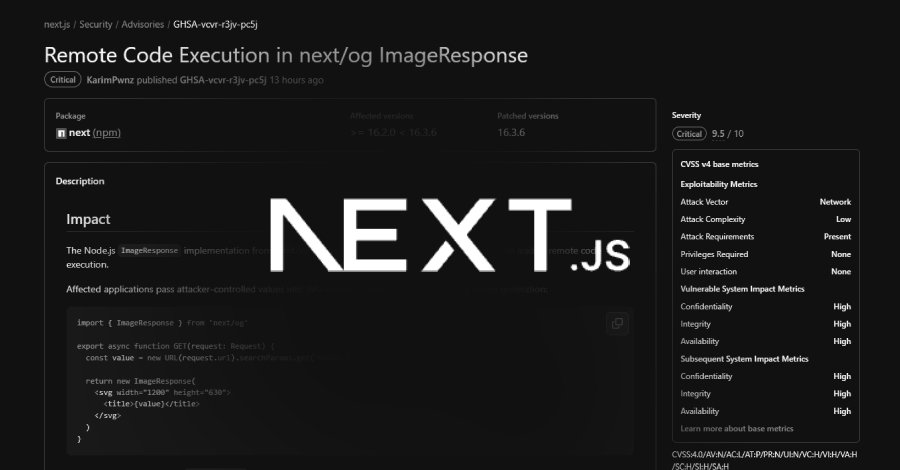
A new security vulnerability in Next.js could enable attackers to execute code on a server through the ImageResponse function, which is responsible for generating Open Graph and other social preview images. According to Vercel, the developer of Next.js, the risk arises when an application incorporates values controlled by an attacker, such as text from the request URL, into the image. The vulnerability has been registered under CVE-2026-1234 and affects all versions of Next.js released before the patch. Vercel fixed the security vulnerability in the latest version on September 22, 2026.
Developers are strongly urged to update their applications to prevent potential attacks. The vulnerability could allow attackers to execute arbitrary code on the server, leading to severe security incidents. This type of attack could be particularly dangerous for companies using Next.js for their web applications. The ability to execute server code opens up numerous options for attackers to steal data or compromise systems. Vercel also noted in its security update that the vulnerability can be exploited through unsafe inputs in the ImageResponse function.
Developers should ensure that all inputs fed into the function are validated and sanitized to minimize the risk of an attack. The response from the developer community regarding the security vulnerability has been swift. Many developers have already implemented updates to protect their applications. Vercel has also provided additional resources to assist developers in identifying and addressing security issues. This vulnerability is not the first to be discovered in popular web frameworks.
Similar issues have been identified in the past with other frameworks, highlighting the need to integrate security practices into software development. Vercel has emphasized that the security of its users is a top priority and that it is continuously working to improve security standards. The discovery of this vulnerability comes at a time when cyberattacks on web applications are increasing. According to the Cybersecurity & Infrastructure Security Agency (CISA), there was a 30% increase in attacks on web applications in 2025 compared to the previous year. Companies are therefore urged to strengthen their security measures and conduct regular updates.
Vercel has also called on the developer community to implement security practices that go beyond mere software updates. This includes regular security audits, training for developers, and the implementation of security policies that ensure all aspects of software development are considered. The security vulnerability in Next.js is another example of the challenges developers face in today’s digital landscape. The need to quickly identify and address security gaps is crucial to maintaining user trust and ensuring the integrity of web applications. Vercel has announced that further security updates are planned in the coming months to continuously improve the platform. The vulnerability was fixed in version 12.3.0 of Next.js, released on September 22, 2026.
💬 Comments (0)
No comments yet. Be the first to comment!